Phishing training for Australian accountants and bookkeepers

Help your practice recognise tax impersonation, unexpected client documents and changes to payment instructions. Build checking habits through training and phishing simulations.

Make suspicious financial requests easier to question

Accounting and bookkeeping teams work with client information, tax correspondence and payment requests. An email that mentions a familiar client or a busy deadline may look plausible while asking the recipient to take an unsafe action.

Use phishing awareness to separate the request from the pressure around it. Train staff to reach the usual portal, confirm changes through a known contact and escalate requests that do not fit your practice's normal process.

Explore automated phishing simulations for recurring practice and employee security training for the learning to reinforce between tests.
Explore phishing training for your practice

Start a business trial and review how the platform fits your team.

Include the people involved in client and payment requests

Use your own procedures to make each discussion specific.

Accountants

Check unusual tax, account-access and client-information requests.

Bookkeepers

Reinforce the process for verifying invoices and changed payment details.

Payroll staff

Question unexpected changes to employee details or instructions.

Client-service teams

Check the context of incoming files and messages before forwarding them.

Practice managers

Keep reporting responsibilities and escalation routes easy to find.

Partners and owners

Model the same verification steps expected of the rest of the practice.

Connect phishing training with practice workflows

Practical examples, feedback and a clear next step.

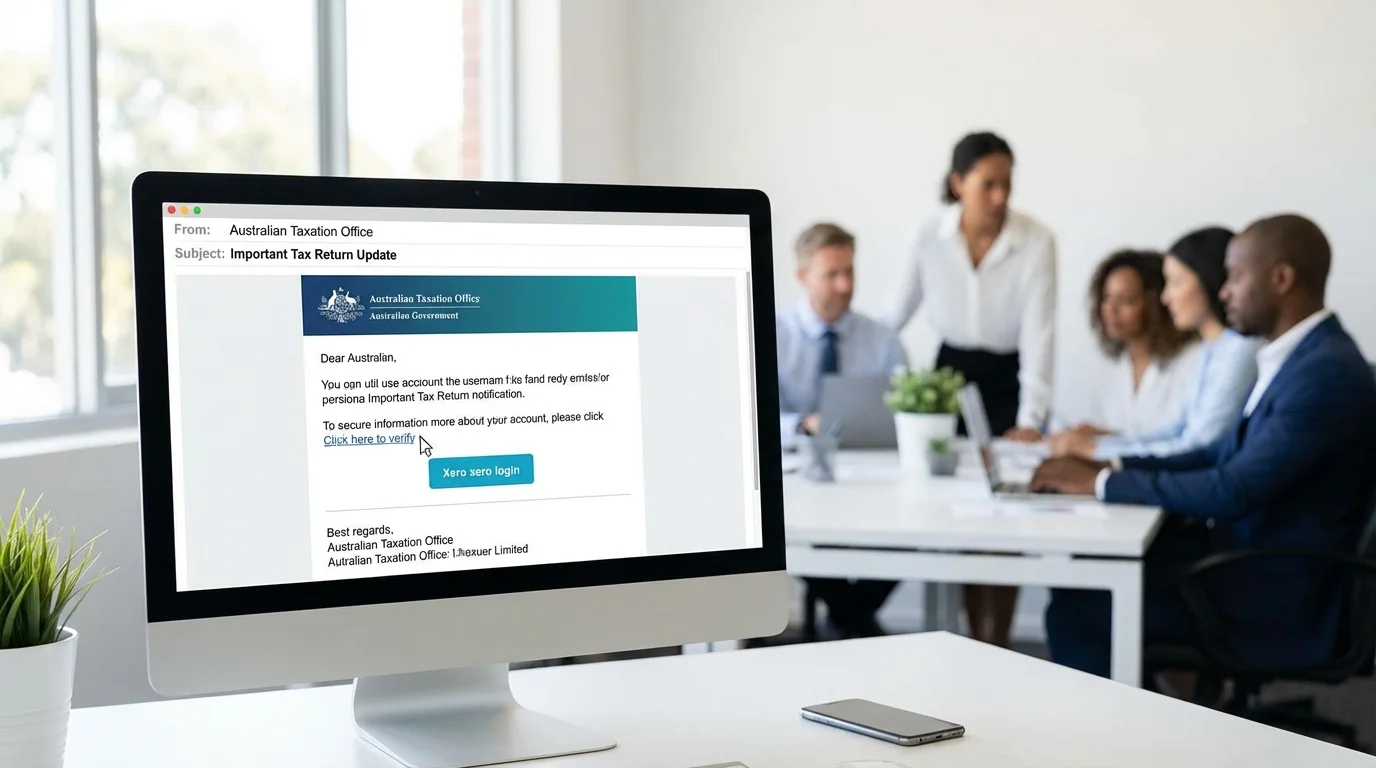
Simulated ATO phishing email example

Question tax and account impersonation

Discuss a message that claims a tax document or account action is waiting. Practise opening the service through its usual trusted route instead of relying on the unexpected message.

Automated scheduling system for phishing tests

Reinforce checking habits over time

Use recurring simulations to revisit the decisions employees make when handling client files, invoices and login requests. Follow up on the specific warning signs in each scenario.

Security awareness compliance report for accountants

Review the topics that need attention

Use testing and training records to guide team discussions. Clarify who verifies payment changes and where staff should report a suspicious message.

Three accounting-workplace situations worth practising

A purported tax notice or myGov message

An email creates urgency around a refund, a document or an account restriction. Use the trusted service or established agent workflow to check the notice, rather than signing in through its link.

A supplier's new bank account

An invoice or follow-up email requests a change to payment details. Verify the change through the practice's approved process and a contact channel already held on file.

An unexpected client document

A message asks staff to open a file or provide a password to view it. Confirm that the client intended to share the document and use the established exchange process.

Use these examples as discussion prompts. Choose simulation scenarios that match your actual systems and responsibilities instead of assuming every role needs the same test.

For an accessible introduction, share our free phishing awareness course. It is available to any person or organisation.

Questions about phishing training for accounting practices

Yes. These are relevant awareness topics for Australian practices. Explain how your team normally accesses trusted services and checks correspondence without relying on an unexpected link.

No. Keep your established authorisations and independent checks. Training helps staff recognise when a request needs to go through those controls.

The public course is available to individuals and organisations of any size. A business trial lets you explore whether simulations and follow-up learning suit your team.

Yes. Share the public course link so they can complete the training themselves. Keep any advice about your own practice's procedures separate and clear.

Build a consistent checking habit across your practice

Explore OutPhish Australia or discuss a starting point for your team.

Start free